How to Run a Private Codex Gateway for Your Company on Official API Keys
Run a private Codex gateway on official API keys: deploy LiteLLM with Docker Compose behind HTTPS, issue one key per employee with budgets, and log usage.
Notes / AI Safety
Topic
Permissions, audit trails, and explainability, so teams can trust AI output and trace problems when they happen.
24
notes
In this topic
Run a private Codex gateway on official API keys: deploy LiteLLM with Docker Compose behind HTTPS, issue one key per employee with budgets, and log usage.
Agent authentication pairs employee and agent IDs per request and intersects gateway and employee rights to stop shared-account data overreach and audit bypass.
Deloitte: 23% of firms use AI agents moderately or more; 74% expected in two years. Only 21% rate governance mature. Four checks without longer approval chains.
Agents on shared workflows belong to the process owner. When the builder leaves, swap credentials, check triggers, clear private memory; if unowned, freeze it.
Agent pilots run on clean data with engineers watching. Production brings messy data, cross-system writes, and real consequences. Five checks before you scale.
AI Agent permissions: ease approval for mail search and summaries; approve sends and calendar edits by default. Fill in a permission table before Always allow.
An AI agent took a wrong action. Stop it and revoke credentials in hour one, roll back by action type, replay the action log, and assign accountability by role.
Test agents in mock companies before CRM access. Tools like Era generate them with mock APIs and MCP endpoints. Retest with real data in staging before launch.
Log agent purpose, builder, owner, systems, credentials, triggers, last run. Tier by data sensitivity and action impact. Disable unowned agents by a deadline.
Agent handoffs may carry malicious external content. Verify originators, limit actions, block internal addresses, and get human approval for high-risk writes.
Agent access by impact: reads, internal drafts, capped writes; humans approve external actions, payments and irreversible operations; upgrade and revocation rules per tier.
China's GB/T 47746-2026 took effect Sept 1, 2026. AI agents may answer order questions; refunds, discounts, and compensation need human or formal sign-off.
Models can make dozens of AI video ads a day; fewer pass brand and platform review. China's labeling rules, Google's AI ad labels, and a pre-scale review gate.
China's AI content labeling rules took effect 2025-09-01. An ad legal ledger needs source, generation process, and license fields, plus who logs each one.
CISA's acting director uploaded a For Official Use Only contract to public ChatGPT. Consumer plans may train on inputs. Redact names, amounts, and seals first.
Codex and Claude Code spend on personal keys won't match finance. Who reconciles, which log fields to keep, and why only gateway-issued credentials work.
First touches, pricing, key accounts, and unclear context go to a human. Routine follow-ups send by rule, with checks on frequency, opt-outs, and approval logs.
Run an enterprise AI pilot in one department on one scored workflow with written go/stop criteria. Giving every employee an AI account first is not a pilot.
Before enabling Grok Bot company-wide, decide who gets access, how approvals are enforced, and what the Audit Log and Action Recording each actually capture.
All Grok Bots on one Cursor account share one cloud computer, files and logins included. Each Bot's screen is a work surface, not a security boundary.
Third-party MCP servers let agents call code on your network. Check the accounts the servers run under, input paths, authentication, version maintenance and credential rotation.
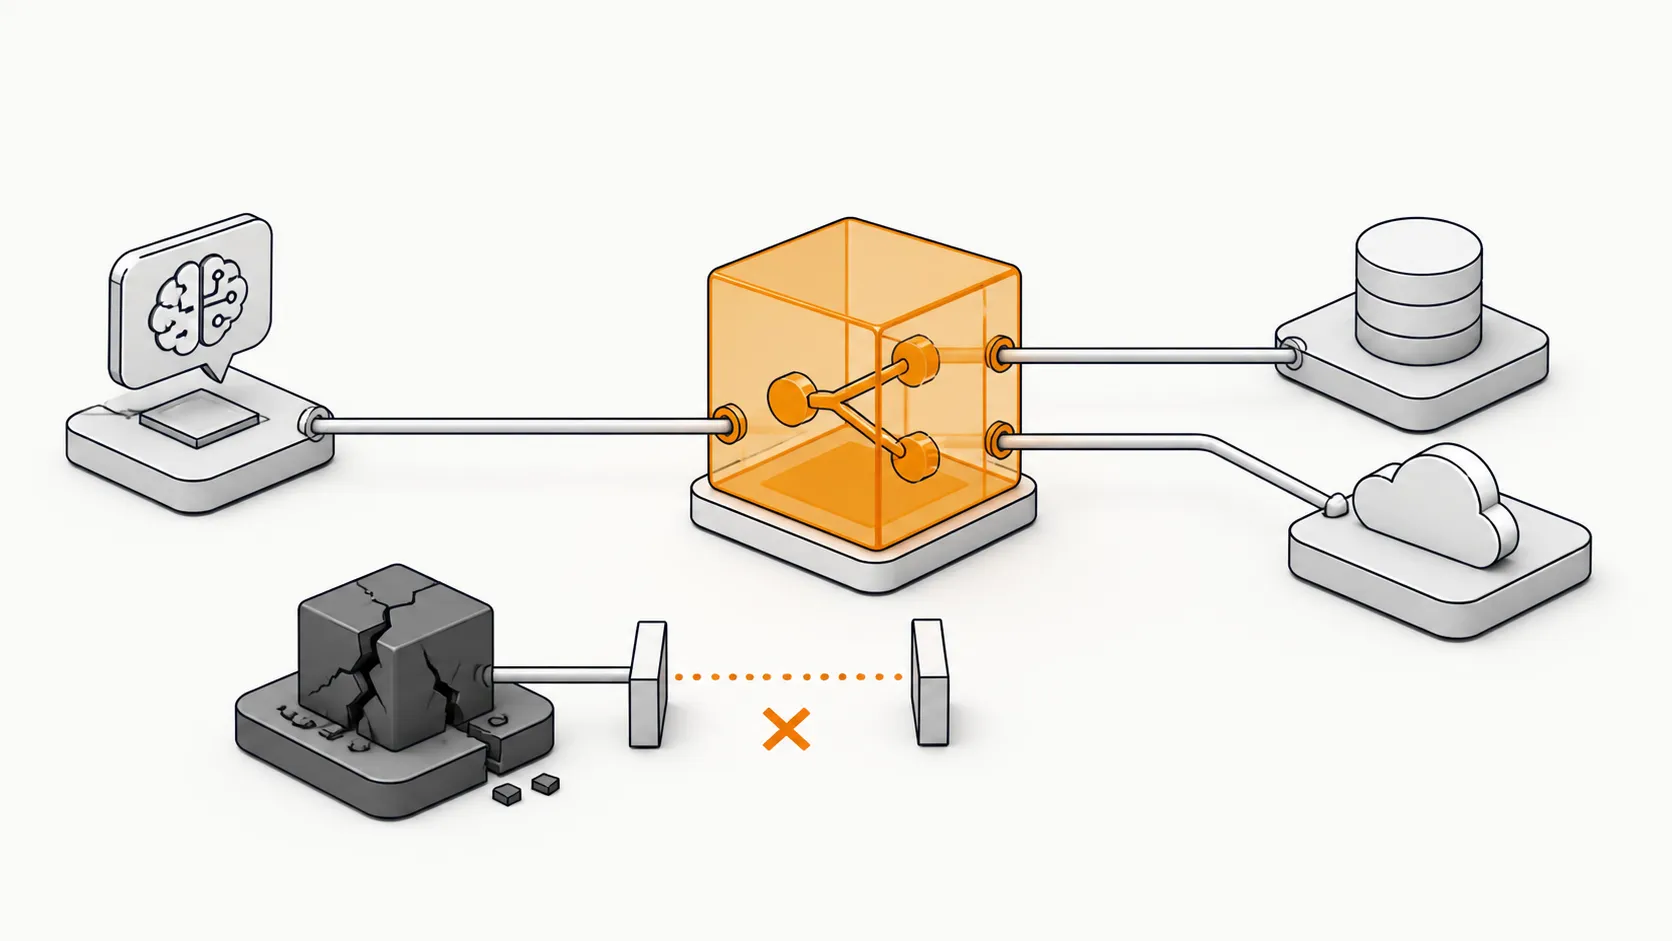
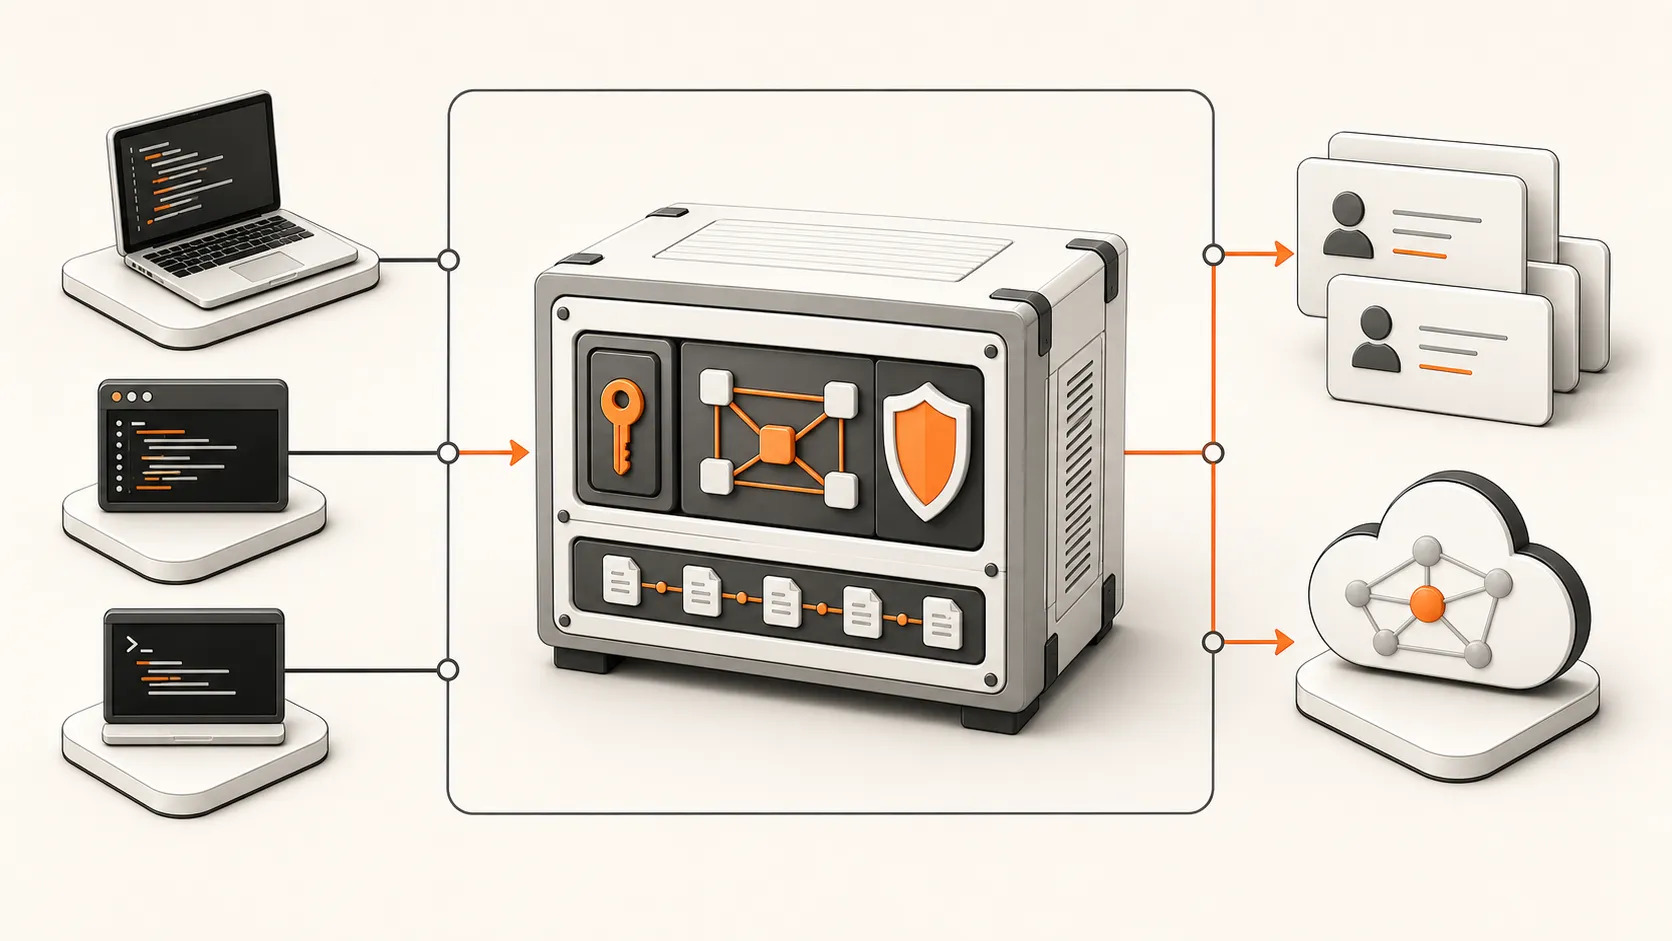
An LLM API gateway gives all of a company's AI calls one entry point for authentication, routing, rate limiting, audit, model fallback, and cost logs.
When every employee buys their own AI account, nobody can see who uses which model or what data leaves. Companies need one trusted relay or gateway instead.
A practical guide to third-party LLM router risk, malicious model output, Agent Full Access, credential theft, sandboxing, and self-managed LLM gateways.
Free. Remote, over video.